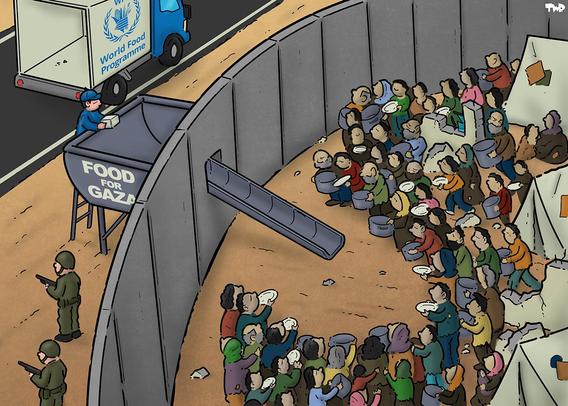
Funding cuts force the World Food Programme to drastically reduce lifesaving assistance in Gaza. Cartoon for Dutch newspaper Trouw.#hunger #starvation #aid #food
Funding cuts force the World Food Programme to drastically reduce lifesaving assistance in Gaza. Cartoon for Dutch newspaper Trouw.#hunger #starvation #aid #food
The hackers stole 11 million email addresses from CAPCOM ID and changed the login passwords for 196 accounts.
Malicious Brotli data can make an application on an official build of Node.js run attacker-supplied code, security researchers at Imperva have demonstrated.
Japanese gaming giant Capcom has confirmed that hackers breached its membership service, CAPCOM ID, exposing more than 11.
Cloudflare reports millions of exploit attempts, while Amazon spotted attackers trying their luck four days before patches landed
U.S. federal investigators pursuing the ShinyHunters hacking group that recently stole highly sensitive data from the FBI have identified executives at two different r…
Patch the Planet connects security researchers, maintainers, and incident responders to help address critical vulnerabilities across open source.
Storm-0940 used ARTEX agentic AI to accelerate a ConnectWise supply chain compromise, enabling application credential abuse across Microsoft 365 environments.
The True Blast Radius of an AI Attack
View CSAF Summary .NET Client Library for SIMATIC S7 Webserver API contains multiple vulnerabilities that could allow an attacker to obtain sensitive information or wr…
When trusted packages are compromised, malicious code can quickly spread throughout and beyond developer environments.
TL;DR: PHP2Shell comprises two critical vulnerabilities that can allow unauthenticated attackers to execute code on affected PHP installations.
AI is expanding faster than anyone can imagine, as organizations race to use AI to gain a competitive advantage. It started with Generative AI.
Two critical flaws in PHP’s request lifecycle can enable unauthenticated remote code execution.
I think what really resonates with me this week is being able to completely turn the tables on perceptions around things like AI being the big bad hacking tool the new…
We already know AI can find vulnerabilities. James Kettle, PortSwigger's Director of Research, wanted to answer a harder question: can an autonomous system invent genu…
Interactive TLS-capable intercepting proxy for traffic analysis.
Relevance: AppSec & traffic inspection
Open-source XDR/SIEM for threat detection and compliance.
Relevance: Detection & response / compliance
Comprehensive scanner for containers, IaC, and dependencies.
Relevance: Cloud & container defenders
Passive subdomain enumeration from dozens of sources.
Relevance: Recon & attack-surface mapping
Template-based vulnerability scanner for massive-scale network scanning.
Relevance: Offensive security & recon
Swiss-army toolkit for network attacks, MITM and recon.
Relevance: Network penetration testing
Graph-based Active Directory relationship explorer for attack paths.
Relevance: Red teams & AD assessment
RE: https://infosec.exchange/@yossarian/117480316228420260so cool that we're now 72+ hours (more if you include the revocation window) into the biggest CA compromise incident ever and Apple still hasn't fixed this
The Phermi ParadoxIf #PHP2Shell is so gnarly and so many systems are vulnerable, why hasn't half the internet fallen over?Couple possibilities:1. The exploit is still non-trivial and building the full attack chain is taking some time.This is at least partially true. I've yet to see a fully reliable proof-of-concept exploit that addresses all versions of PHP. Calif and Wiz showed exploit videos against targets. They didn't show what pregaming they did to prepare the exploit for those specific targets. So far, it seems like some prior work is necessary to get proper offsets, heap layouts, and payload shapes to exploit properly.And that's assuming the mod_php SAPI, which responds differently to this than PHP-FPM.2. Patching was aggressive and major targets had time to get in front of this.For larger orgs, I believe this is accurate. The message was clear enough, and there was time enough to get any org with a half-awake IT team to circle the wagons. Patching isn't done, surely, but I think the most enticing targets for notable attacks probably moved quickly.It's also worth noting that status dashboards like this are mostly a fairy tale. Look at the bottom for some whopper disclaimers. OS backports to versions other than PHP's official patched versions will muddy the picture, as will the 50% of PHP services that don't report versions. I'm not saying most of the internet is patched; I'm just sayingBut let's not ignore the alternative:3: The exploited won't know it's happening and won't report it.This is hardly a new phenomenon PHP sites have been exploited for years without anyone noticing (see: Slot Gacor). Exploitation won't look like the internet blinking off. It'll look like a bunch of gambling pages and piracy hosted on school and municipal government websites. Such attacks can lie quietly on PHP sites for years before anyone bothers to look.
RE: https://infosec.exchange/@munin/117488365783668802"In this case the court starts by stating, "This case presents the question of whether a bee is like a cow." The court held that bees are not like cows."
Until you’re agentic swarm can hack into the government and release the Epstein files, I will not be impressed
So we got super lucky and hired @zeroSteiner over in VulnCheck-land, and after he and our exploit dev team got RCE working on a range of ASLR-enabled x86 systems last night, we forced him to agree to do a webcast on #php2shell hackery next week. Someone please help him, he's trapped on company Zooms and can't escape. OR, join us October 28 @ 1 PM ET! https://wwv.vulncheck.com/in-the-wild-with-vulncheck-webinar-seriesWe've been watching exposure numbers shift and Canary hits roll in. Our research crew has been merrily swimming in the AI PoC swamp, since we are masochists and review literally all the exploit code on GitHub. The first functional *public* ASLR bypass PoC our team tested cropped up this afternoon, so things might be about to go 📈 Anyway, it'll be fun and technical and the webinar equivalent of lying down on the floor and going "man wtf" for 45 minutes. JOIN US.