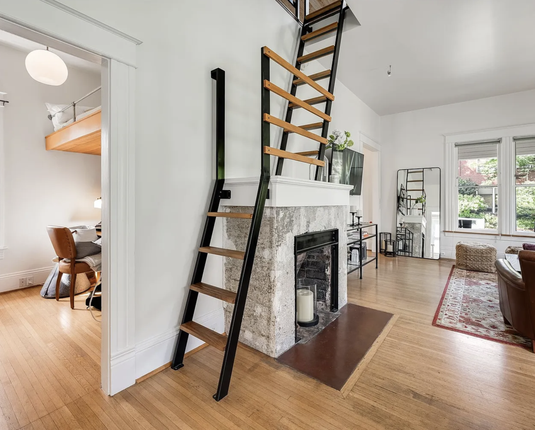
I can't say that I've seen this before. A ladder that goes across a mantelpiece, and a bunk bed with the ladder going through the platform. https://www.zillow.com/homedetails/1124-SE-35th-Ave-Portland-OR-97214/300093774_zpid/
I can't say that I've seen this before. A ladder that goes across a mantelpiece, and a bunk bed with the ladder going through the platform. https://www.zillow.com/homedetails/1124-SE-35th-Ave-Portland-OR-97214/300093774_zpid/
Google on Thursday released security updates to patch 12 vulnerabilities, including one that has come under active exploitation in the wild.
Miscreants use chained zero days to pwn boxen as third-party SOCs say further attacks 'almost certain'
Hacker group published roughly 550GB of data after MAG reportedly refused to pay a ransom demand; the group says it gained access via exposed admin keys.
Hewlett Packard Enterprise (HPE) has patched a critical vulnerability in the ArubaOS-CX network operating system that could lead to remote code execution. [...]
Authorities in Australia have arrested two men believed to be members of TeamPCP, a prolific cybercrime and data extortion group blamed for perpetrating the longest ru…
Astra is the first OpenAI model to meet the Critical cybersecurity capability threshold under the Preparedness Framework, with stronger safeguards for release.
CISA has added seven new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. <a href="https:
Critical SQL Injection in Metabase via Password Reset: CVE-2026-72898
Microsoft Threat Intelligence observed a human-operated intrusion campaign that abuses Microsoft Teams external collaboration to impersonate IT support, gain remote ac…
Detect exposure to new vulnerabilities the moment they are published with Wiz CVA
TLDR: The attacks most likely to go undetected are the ones that never touch disk.
Originally published by Darktrace. Findings from our annual survey of 1,500+ cyber professionals reveal that security leaders are confronting a surge in AI-driven atta…
It does feel like I've bitten off too much and am now chewing like crazy this week.
We already know AI can find vulnerabilities. James Kettle, PortSwigger's Director of Research, wanted to answer a harder question: can an autonomous system invent genu…
AI applications can pass security scans yet remain exploitable through chained attacks across models, tools, data, and business workflows.
AIR's platform can discover agents running at a company, continuously vets any skills and add-ons they use, and blocks any unwanted behavior.
Open-source XDR/SIEM for threat detection and compliance.
Relevance: Detection & response / compliance
Passive subdomain enumeration from dozens of sources.
Relevance: Recon & attack-surface mapping
Comprehensive scanner for containers, IaC, and dependencies.
Relevance: Cloud & container defenders
Template-based vulnerability scanner for massive-scale network scanning.
Relevance: Offensive security & recon
Interactive TLS-capable intercepting proxy for traffic analysis.
Relevance: AppSec & traffic inspection
Swiss-army toolkit for network attacks, MITM and recon.
Relevance: Network penetration testing
Graph-based Active Directory relationship explorer for attack paths.
Relevance: Red teams & AD assessment
Since Berlin is doing Berlin things and mostly just warning people who work in the government to beware of generative AI phishing based on the stolen information from the (perhaps) latest hack, I'd like to take a moment to say: The residents of Berlin who *don't* work in or above the hacked departments should *also* be extra-careful right now to verify the normalcy of any contacts that don't 100% line up with expectations.There's no such thing as a hack of two working chunks of gov that exfiltrates enough employee data to be worth blackmail, but magically doesn't leak regular citizen data as well.
RE: https://infosec.exchange/@stalkphish_io/116894695275584458Our scanner is now live!We opened it for beta testers -> drop us an email contact---stalkphish.com for an access.
ASN: AS8075Location: Oslo, NOAdded: 2026-08-31T10:58#shodansafari #infosec
RE: https://infosec.exchange/@sparklepanic/117182321521366621still very proud of this photoit's now part of my top 10 photos on my website
JFrog Artifactory CVE-2026-82329 Critical Flaw🔗 https://cybersecurefox.com/en/jfrog-artifactory-cve-2026-82329-critical-vulnerability#JFrog #Artifactory #CVE-2026-82329 #critical #vulnerability #CVSS #9.8 #software #supply #chain